SQL Injection in TTD Web Application
Target
Organization: Tirumala Tirupati Devasthanams (TTD)
Affected application: apps.tirumala.org
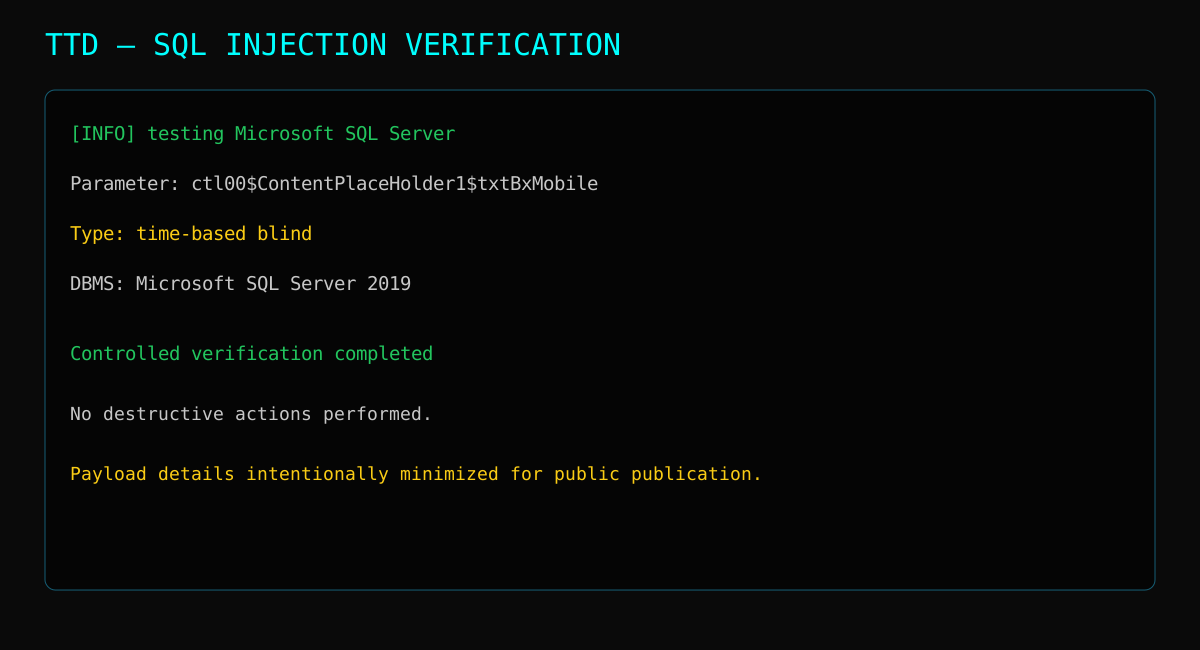
Affected parameter: ctl00$ContentPlaceHolder1$txtBxMobile
Verification
The finding was manually identified and subsequently verified with SQLMap in a controlled, non-destructive manner. The backend was identified as Microsoft SQL Server 2019.
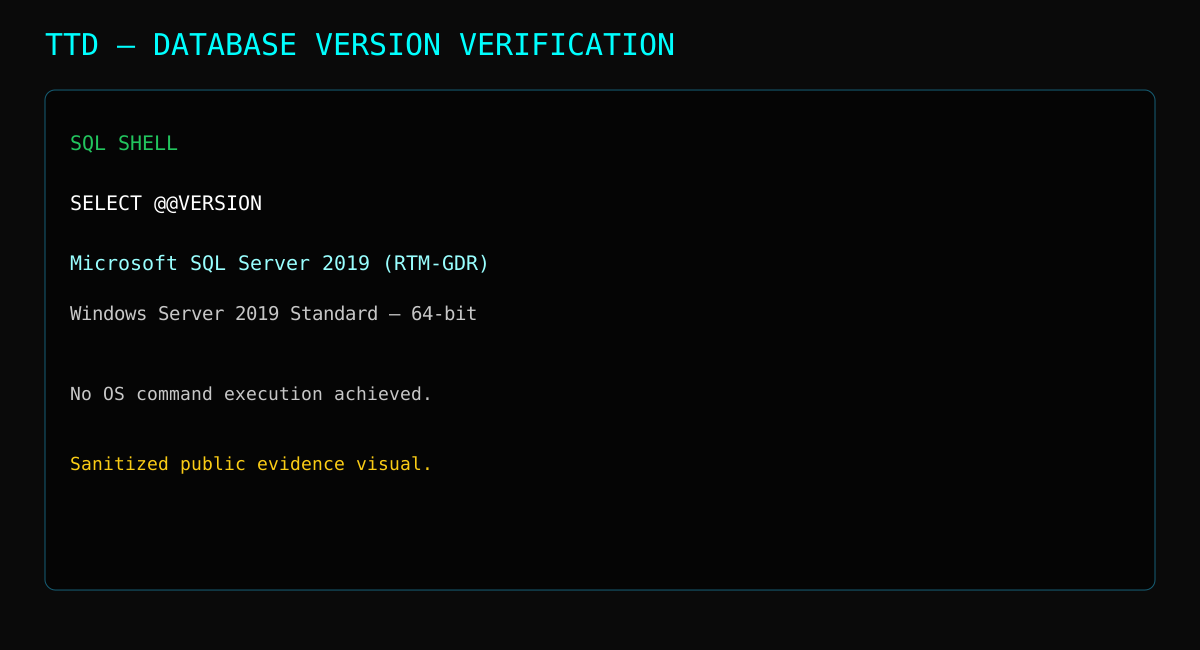
The researcher verified database query execution and retrieved the SQL Server version using SELECT @@VERSION. No operating-system command execution, destructive modification, deletion, or intentional sensitive-data extraction was performed.
Evidence
Sanitized SQL injection verification screenshots are prepared for the public research archive. Raw requests and sensitive values are not published.
SQLMap verification
SQL Server version verification
Disclosure Timeline
23 Jul — Responsible disclosure submitted to CERT-In.
Verification — Microsoft SQL Server 2019 and controlled query execution verified.
Status — Finding remains under responsible disclosure.
Recommended Remediation
- Use parameterized SQL statements.
- Apply least-privilege database accounts.
- Review related endpoints for injection.
- Maintain appropriate monitoring and defensive controls.