Improper Session Invalidation After Logout
Finding
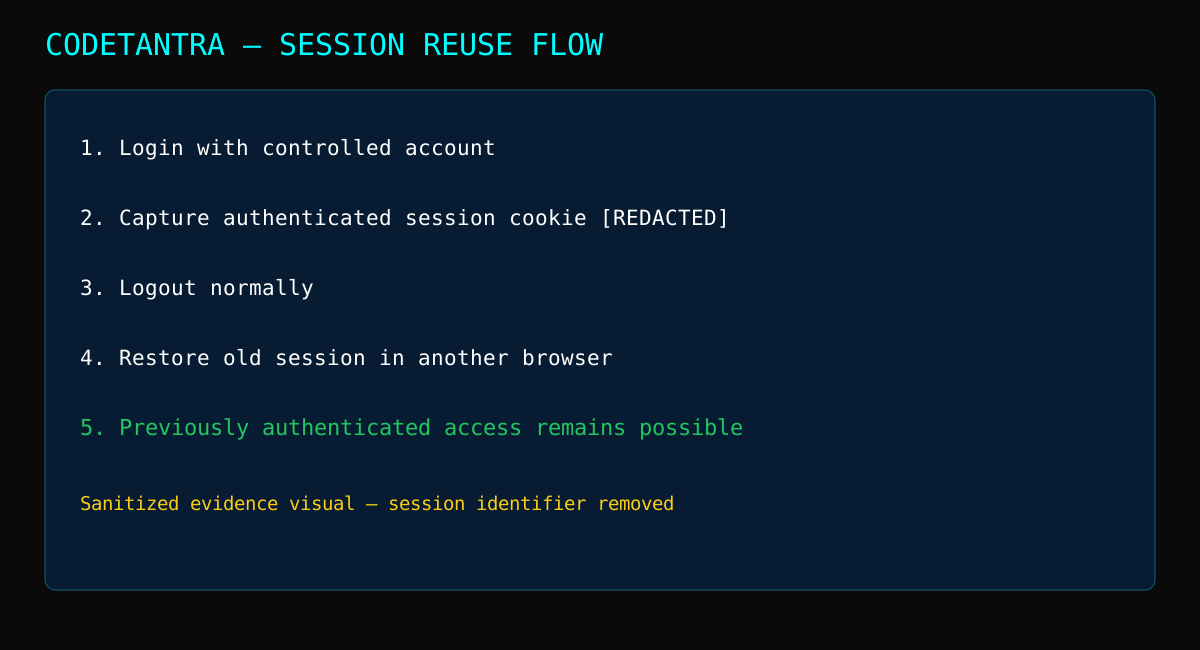
A previously issued authenticated session cookie remained valid after logout. The issue was reproduced by capturing the session in one browser, logging out, then restoring the session in another browser.
Impact
An attacker who obtains a valid session before logout could potentially continue accessing the account after the victim believes the session has been terminated.
Testing
Testing was limited to an account controlled by the researcher. No third-party accounts or data were accessed.
Evidence
The original report included a screen recording demonstrating session reuse. Public evidence is intended to use sanitized frames only; credentials and session identifiers are excluded.
Disclosure Timeline
26 Jun — Report submitted to CERT-In.
27 Jun — Follow-up supplied for verification.