JWT Remains Valid After Logout and Allows DNS API Token Creation
Research Metadata
Disclosure status: Fixed
Finding
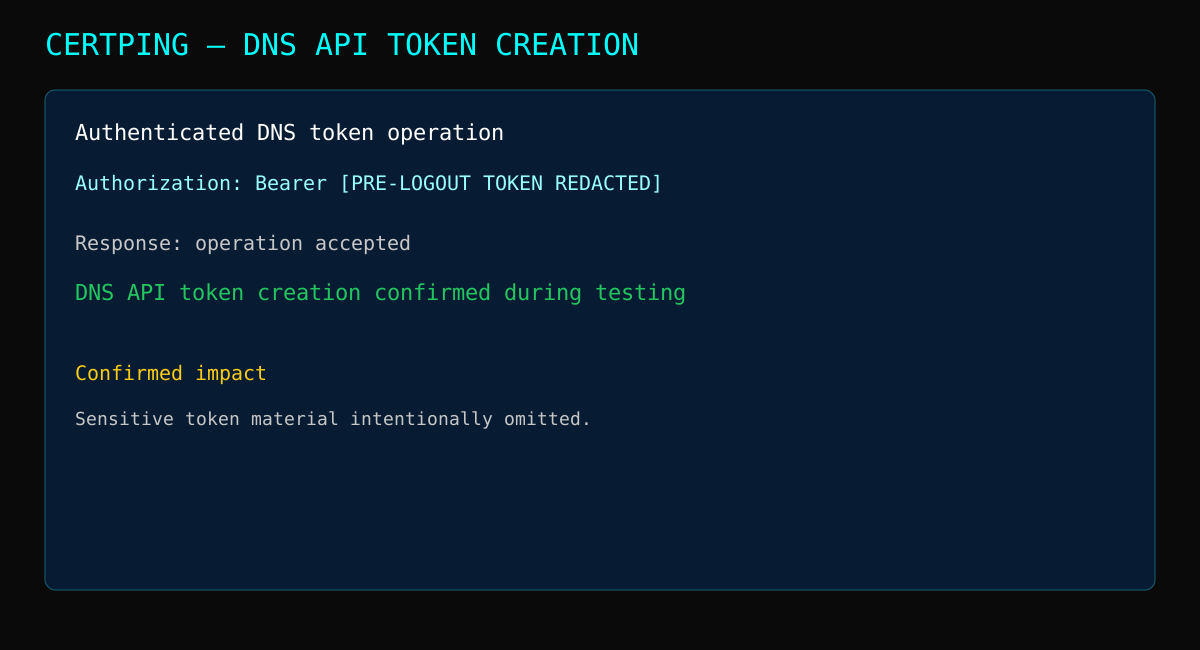
The authenticated access JWT continued to be accepted after logout. During testing, the same pre-logout token remained usable for authenticated functionality, including DNS API token creation.
Confirmed Scope
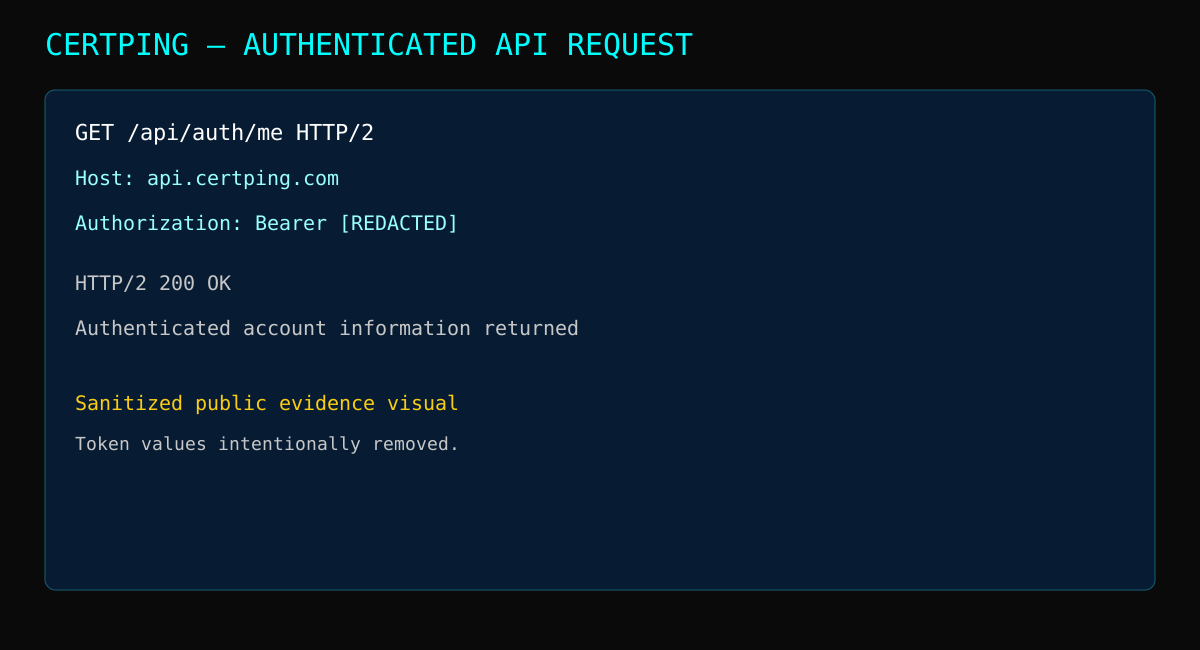
The confirmed endpoints/functionality included GET /api/auth/me and DNS API token creation. The report did not claim access to the entire authenticated application.
Vendor Response & Remediation
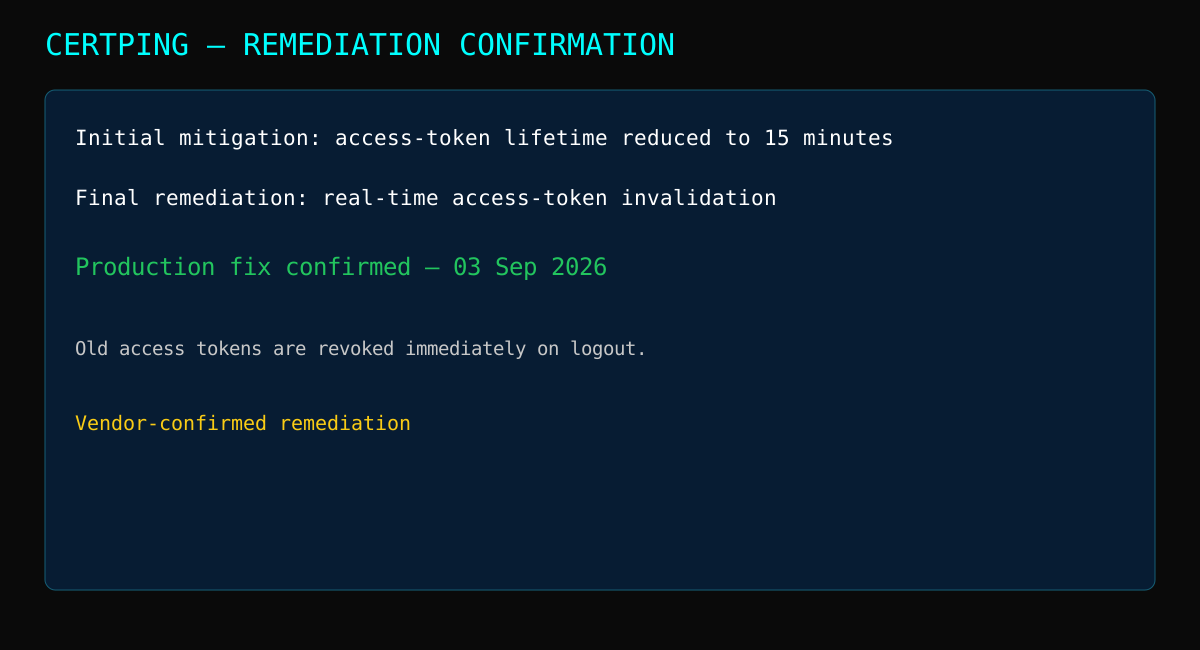
CertPing confirmed that the refresh token was already invalidated at logout, while the access token was long-lived. The team first reduced access-token lifetime to 15 minutes, then decided to implement real-time access-token invalidation.
On 3 September 2026, CertPing confirmed that real-time access-token invalidation had been deployed to production so tokens are revoked immediately upon logout.
Evidence
Sanitized evidence from the original report is prepared for publication. Authentication tokens and other sensitive values must remain redacted in the public archive.
Authenticated API request
DNS token creation
Vendor remediation response
Disclosure Timeline
20 Aug 2026 — Vulnerability reported.
20 Aug 2026 — Engineering confirmed the access-token gap.
24 Aug 2026 — Real-time invalidation selected.
03 Sep 2026 — Production fix confirmed.